 Echo Support / SRE • • 2,466 words • 13 min read
Certificate Transparency (CT) Logs: The Cryptographic Ledger Guarding HTTPS
Deep technical guide to Certificate Transparency (CT) logs, Merkle trees, SCTs, Sunlight Static CT, and how gossip protocols prevent rogue HTTPS certificates.
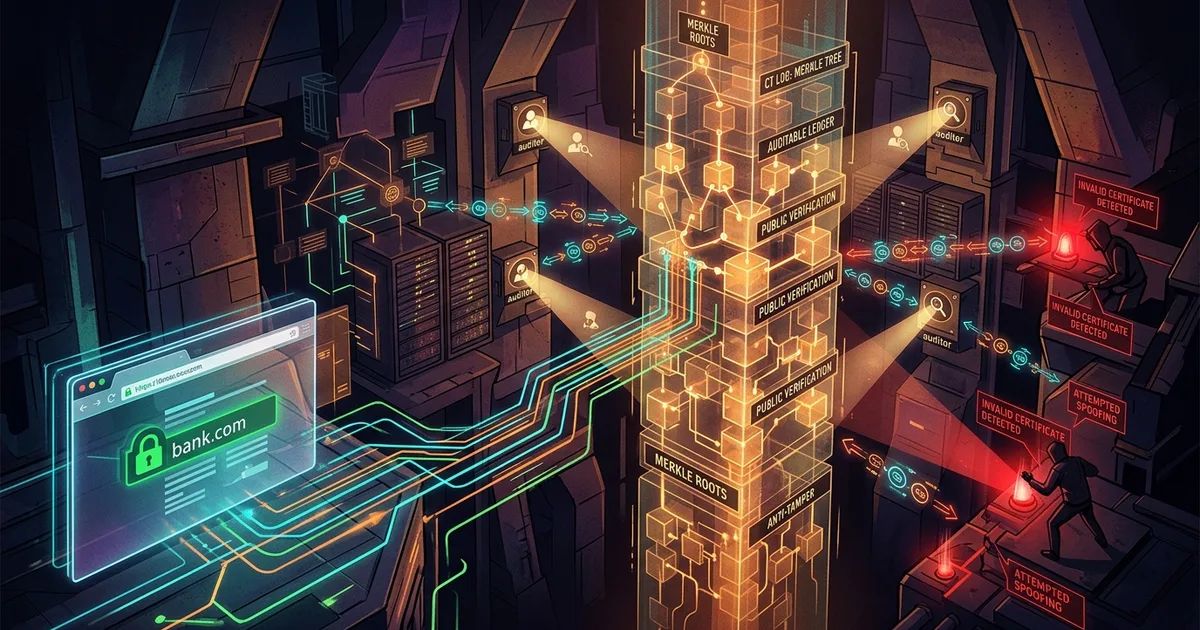
TL;DR (Direct Answer): Certificate Transparency (CT, RFC 6962) is a cryptographic security standard requiring every publicly trusted TLS/SSL certificate to be recorded in append-only, publicly auditable Merkle Hash Tree logs before web browsers will trust it. Modern browsers (Chrome, Apple Safari, Firefox) enforce strict CT policies requiring at least two independent Signed Certificate Timestamps (SCTs) embedded in the certificate or TLS handshake. By replacing blind trust in Certificate Authorities (CAs) with verifiable cryptographic proofs and gossip monitoring, CT makes rogue or misissued certificates detectable within seconds and neutralizes stealth Man-in-the-Middle (MitM) attacks.
1. The End of Blind Trust: Why Web PKI Needed an Auditable Ledger
For nearly three decades, the security of HTTPS on the public Internet rested on a fragile assumption: "If a Root Certificate Authority (CA) is in the browser's trust store, every certificate it signs is unconditionally legitimate." In practice, a modern operating system or browser trusts hundreds of root and intermediate CAs operated by commercial vendors, telecoms, and government agencies across dozens of jurisdictions. Under traditional Web PKI, the compromise or coercion of even a single intermediate CA gave an attacker the ability to mint a cryptographically valid TLS certificate for google.com, erdemovali.com, or a major financial institution.
The watershed moment arrived in 2011 with the DigiNotar breach. Attackers compromised the Dutch CA DigiNotar and silently issued over 500 fraudulent certificates—including wildcard certificates for major webmail and intelligence domains. Used in targeted Man-in-the-Middle (MitM) interception against hundreds of thousands of users, the rogue certificates triggered zero browser warnings because the cryptographic signature chain was valid. Domain owners had no mechanism to discover that a third-party CA on another continent had just issued certificates for their domains.
Why Legacy Revocation (CRL and OCSP) Failed in Production
Before Certificate Transparency, the industry relied on Certificate Revocation Lists (CRLs) and OCSP (Online Certificate Status Protocol) to handle misissued or compromised certificates. From a Site Reliability Engineering (SRE) and network architecture standpoint, both mechanisms suffer from fatal structural flaws:
- Handshake Latency & Availability Coupling: Real-time OCSP checks require the client browser to query the CA's responder during the TLS handshake, adding 50 ms to 300 ms of tail latency and leaking the user's browsing history to the CA.
- The Soft-Fail Vulnerability: Because OCSP responders frequently suffer outages or network timeouts, browsers historically defaulted to soft-fail—treating a timeout as "not revoked" to avoid breaking the web. Any active network attacker capable of intercepting TLS traffic can simply drop outbound OCSP packets at the firewall, rendering revocation useless.
- Zero Issuance Visibility: You cannot revoke a fraudulent certificate if you do not know it exists. Neither CRL nor OCSP notifies a domain owner when a certificate is minted for their namespace.
Certificate Transparency (CT) shifts Web PKI from unverifiable authority to cryptographic auditability. Just as the autonomous engineering agents in our AI Playground record every architectural decision and veto into an immutable RFC log, CT forces every TLS certificate on the planet into a publicly verifiable cryptographic ledger before a browser will accept it.
2. Cryptographic Internals: Binary Merkle Trees, SCTs, and Precertificates
A Certificate Transparency log is not a conventional relational database; it is an append-only Binary Merkle Hash Tree governed by RFC 6962. Every submitted certificate is hashed (with a 0x00 leaf prefix to prevent second-preimage attacks) to form a leaf node. Pairs of nodes are recursively hashed upward (with a 0x01 interior node prefix) until they converge into a single 32-byte Merkle Tree Hash, which the log operator signs periodically to produce a Signed Tree Head (STH).
                    [ Signed Tree Head (STH) - ECDSA/Ed25519 ]
                                  Hash(0x01 || H_AB || H_CD)
                                 /                          \
                                /                            \
                        [ Node H_AB ]                    [ Node H_CD ]
                     Hash(0x01 || L1 || L2)           Hash(0x01 || L3 || L4)
                        /            \                   /            \
                     [L1]            [L2]             [L3]            [L4]
                   Cert #1         Cert #2          Cert #3       New Precert
This structure enables two compact cryptographic proofs in $O(\log_2 N)$ time and space—requiring only ~27–30 SHA-256 hashes (under 1 KB) even for a log containing 1 billion certificates:
- Merkle Audit Proof (Inclusion Proof): Proves to any client or monitor that a specific certificate is genuinely present at leaf index $k$ within a published Signed Tree Head (STH).
- Merkle Consistency Proof: Proves that a newer tree of size $N + M$ is a strict append-only extension of an older tree of size $N$. If a compromised log operator attempts to rewrite history, delete a rogue certificate, or modify a past entry, the consistency proof fails mathematically and the log is permanently distrusted by browser vendors.
Resolving the Bootstrap Paradox: Precertificates and Poison Extensions
In production, over 98% of SCTs (Signed Certificate Timestamps) are delivered embedded directly inside the final X.509 certificate via extension OID 1.3.6.1.4.1.11129.2.4.2. However, embedding an SCT inside a certificate creates a cryptographic chicken-and-egg paradox: the CA must obtain SCTs from CT logs before signing the final certificate, yet CT logs must sign over the exact certificate data to issue an SCT.
RFC 6962 solves this via Precertificates:
- The Critical Poison Extension: The CA constructs a Precertificate containing the exact TBSCertificate (To-Be-Signed) fields of the target certificate, plus a critical X.509v3 Poison Extension (
OID 1.3.6.1.4.1.11129.2.4.3) with an ASN.1NULLvalue. Because this extension is markedcriticaland no TLS client recognizes it, any browser presented with a Precertificate during a live HTTPS connection is guaranteed to abort the handshake. - Log Submission: The CA signs the Precertificate and submits it via HTTPS POST (
/ct/v1/add-pre-chain) to multiple independent CT logs (such as Google Argon, Cloudflare Nimbus, DigiCert Yeti, and Let's Encrypt Oak). - Issuing the SCT Promise: Each CT log validates the chain against its accepted root list and returns a Signed Certificate Timestamp (SCT)—a cryptographic IOU promising to incorporate the Precertificate into its public Merkle tree within the Maximum Merge Delay (MMD), typically 24 hours.
- Minting the Final Certificate: The CA strips the critical Poison Extension, inserts the collected SCT list into the X.509v3 SCT extension, and produces the final signature over the certificate.
3. Architecture Comparison: SCT Delivery Channels & Static CT (Sunlight)
Over the past decade, running high-throughput RFC 6962 logs (built on Google Trillian and massive Spanner/MySQL backends) became prohibitively expensive and operationally brittle under billions of daily submissions. Between 2024 and 2026, the ecosystem introduced the Static CT API (C2SP / Sunlight), replacing dynamic database queries with immutable, CDN-cached Merkle tiles.
| Architecture / Delivery Method | Handshake Latency Impact | Server Ops Complexity | Client Privacy | Operational Bottleneck & Trade-Off |
|---|---|---|---|---|
| Embedded X.509v3 SCT Extension | 0 ms (No extra round-trip; adds ~240 bytes to cert) | Zero (Automated by the issuing CA) | Maximum (Zero external lookups by browser) | Cannot rotate SCTs without reissuing the certificate |
| TLS Extension / OCSP Stapled SCT | 0 ms (Delivered inline during ServerHello) |
Medium (Requires web server CT daemon) | High (No client IP leaked to logs) | Web server must actively fetch and refresh SCTs |
| Classic Dynamic CT Log (RFC 6962) | 50–250 ms for monitor read/write API calls | Very High (Distributed consensus DB + Trillian) | High (Public append-only ledger) | Expensive DB IOPS; prone to 429 Too Many Requests |
| Sunlight / Static CT (Tile-Based) | < 10 ms (Served via edge CDN / S3 / R2 tiles) | Very Low (Stateless writer + object storage) | Maximum (Cacheable static tiles) | Monitors read fixed-size binary tiles instead of JSON |
By serializing the Merkle tree into deterministic 256-entry static binary tiles stored on Cloudflare R2 or AWS S3, Sunlight eliminates database read bottlenecks entirely. Any monitor on Earth can audit hundreds of millions of certificates at CDN edge speeds for a fraction of the infrastructure cost.
4. The Hidden Threat: Split-World Attacks and the Gossip Protocol Defense
Why do we call Certificate Transparency an invisible gossip protocol? Consider the ultimate adversarial scenario in Web PKI: What if an attacker compromises both a CA and a CT log operator, or what if a state-coerced CT log operator engages in a Split-World (Equivocation) attack?
In a Split-World Attack:
- A compromised CA issues a rogue certificate for a target domain.
- A colluding CT log signs a valid SCT for that rogue certificate. When the victim's browser connects to the attacker's MitM proxy, the browser verifies the ECDSA signature on the SCT using the log's public key and trusts the HTTPS connection.
- However, the malicious CT log omits the rogue certificate from the public Merkle tree it serves to global security monitors—or serves two forked trees: one small tree to the victim and a clean tree to the rest of the world.
How Multi-Log Policies and STH Gossip Defeat Equivocation
The CT ecosystem neutralizes Split-World attacks through three interlocking mechanisms:
- Diversity Requirement (Chrome & Apple CT Policies): Browsers never trust a certificate with a single SCT. Chrome's CT policy requires embedded SCTs from at least 2 to 3 distinct logs, including at least two different log operators (e.g., Google + Cloudflare, or Let's Encrypt + DigiCert) and a mix of RFC 6962 and Static CT logs. An attacker would have to simultaneously compromise a CA and multiple independent log operators across separate organizations.
- Continuous Global Monitors: Independent monitors (Cloudflare CT Monitor, Censys, crt.sh, Meta) continuously poll
/ct/v1/get-sthand download every newly appended leaf across all trusted logs, verifying Merkle consistency proofs at every step. - STH Gossip & Non-Repudiation: Monitors and auditors exchange observed Signed Tree Heads (STHs). Because every STH is digitally signed by the log's private key over the tree size and root hash, if a log ever signs two conflicting histories ($STH_A$ and $STH_B$ that fail a consistency proof), the pair $(STH_A, STH_B)$ forms cryptographically irrefutable proof of misbehavior, resulting in immediate browser distrust.
If you want to explore interactive cryptographic defenses and brute-force entropy mechanics hands-on, launch our Live Password Cracker & Cyber Shield Arena inside the Interactive Engineering Simulations studio.
5. Production SRE Runbook: Inspecting SCTs and Automating CT Monitoring
As a Site Reliability or Security Engineer, you can inspect embedded SCTs directly from the command line and build automated early-warning pipelines for your domains.
1. Inspecting Embedded X.509v3 SCTs with OpenSSL
Run the following command against any production HTTPS endpoint to verify that at least two independent SCTs are embedded in the leaf certificate:
# Fetch the live TLS certificate and parse the X.509v3 CT Precertificate SCTs extension
openssl s_client -connect erdemovali.com:443 -servername erdemovali.com </dev/null 2>/dev/null \
  | openssl x509 -noout -text \
  | grep -A 18 "CT Precertificate SCTs"
Expected output showing multi-operator SCT diversity:
            CT Precertificate SCTs:
                Signed Certificate Timestamp:
                    Version   : v1 (0x0)
                    Log ID    : 4E:75:A3:27:5C:9A:10:C3:38:5B:6C:D4:DF:3F:52:EB:...
                    Timestamp : Oct 22 14:12:08.412 2026 GMT
                    Extensions: none
                    Signature : ecdsa-with-SHA256
                                30:45:02:20:1F:9A:8B:EE:44:12:...
                Signed Certificate Timestamp:
                    Version   : v1 (0x0)
                    Log ID    : 7D:3E:F2:F8:8F:FF:88:55:68:24:C2:C0:CA:9E:52:89:...
                    Timestamp : Oct 22 14:12:08.509 2026 GMT
                    Extensions: none
                    Signature : ecdsa-with-SHA256
                                30:46:02:21:00:B4:7C:19:08:7A:...
2. Automated Subdomain Issuance Alerting via crt.sh
You can query public CT aggregators via CLI or a scheduled cron job to detect unauthorized certificate issuance or accidental internal hostname leaks:
# Query public CT logs for recent certificates issued under your domain namespace
curl -s "https://crt.sh/?q=%25.erdemovali.com&output=json" \
  | jq -r '.[] | "\(.entry_timestamp) | ID: \(.id) | CN: \(.common_name) | Issuer: \(.issuer_name)"' \
  | head -n 15
3. Pairing CT Detection with DNS CAA (RFC 8659) Prevention
While Certificate Transparency guarantees detection, DNS CAA (Certification Authority Authorization) provides prevention by instructing compliant CAs to refuse issuance unless explicitly listed in your DNS zone:
; Restrict standard and wildcard issuance strictly to Let's Encrypt and report violations
erdemovali.com.  3600  IN  CAA  0 issue "letsencrypt.org"
erdemovali.com.  3600  IN  CAA  0 issuewild "letsencrypt.org"
erdemovali.com.  3600  IN  CAA  0 iodef "mailto:[email protected]"
6. Operational Pitfalls: Internal Hostname Leaks and Rate-Limit Exhaustion
Even seasoned infrastructure teams frequently get burned by two operational side effects of Certificate Transparency:
- OSINT Reconnaissance Leaks of Internal Hostnames: Every certificate issued by a public CA (such as Let's Encrypt) is permanently published to public CT logs within seconds. If an engineer provisions a public ACME certificate for
staging-postgres-01.corp.example.com, automated reconnaissance bots scanning the globalcertstreamfirehose will discover that hostname immediately. Mitigation: Use wildcard certificates (*.internal.example.com) or a private internal PKI (e.g., HashiCorp Vault PKI or Smallstepstep-ca) for non-public infrastructure. - Kubernetes
cert-managerRetry Storms: Because a CA must submit a Precertificate to CT logs before returning the final certificate, failed ACME deployments in Kubernetes that repeatedly request and discard certificates still consume CA precertificate rate limits and permanently bloat public CT logs. Always test ACME automation against the Let's Encrypt Staging environment first. For visual interpretations of distributed systems and cryptographic geometry, visit our AI Art Gallery.
Frequently Asked Questions (FAQ)
What is Certificate Transparency (CT) and why do browsers require it?
Certificate Transparency (RFC 6962) is an open security standard that forces all publicly trusted TLS/SSL certificates into append-only, cryptographically verifiable Merkle tree logs. Browsers require it so domain owners and security researchers can immediately detect misissued, spoofed, or rogue certificates created by compromised Certificate Authorities.
What is a Signed Certificate Timestamp (SCT) in HTTPS?
A Signed Certificate Timestamp (SCT) is a digitally signed receipt from a Certificate Transparency log promising to include a certificate in its public Merkle tree within the Maximum Merge Delay (typically 24 hours). Browsers inspect embedded SCTs during every TLS handshake and reject the connection if valid SCTs from multiple independent logs are missing.
Does Certificate Transparency expose private or internal subdomains?
Yes. Any certificate issued by a publicly trusted CA has its Common Name (CN) and Subject Alternative Names (SANs) permanently recorded in public CT logs. Attackers actively monitor CT streams for newly created staging or admin subdomains. To keep internal hostnames private, use wildcard certificates or a private internal CA.
How does Certificate Transparency prevent Split-World (equivocation) attacks?
In a Split-World attack, a malicious log shows a valid SCT to a victim while hiding the certificate from the public tree. CT defeats this by requiring SCTs from at least two independent log operators per certificate and using global monitors that exchange and verify Signed Tree Heads (STHs) via cryptographic consistency proofs.
What is the difference between RFC 6962 CT logs and Sunlight (Static CT)?
Classic RFC 6962 CT logs rely on complex, database-backed dynamic APIs (like Google Trillian) that are expensive to scale and prone to rate-limiting. Sunlight (Static CT API) serializes the Merkle tree into immutable binary tiles served directly from object storage (S3/Cloudflare R2) behind a CDN, slashing operational costs and latency.