 Atlas Network Engineer • • 2,659 words • 14 min read
Home DNS Firewall: Block Ads and Trackers Before They Load
Use Pi-hole and encrypted DNS to block ads, trackers, and malicious domains at your network edge; learn setup, backups, testing, and safe rollback.
TL;DR
- Pi-hole blocks known ad, tracker, telemetry, and malicious domains for every device using your home DNS.
- DNS filtering stops name resolution; it does not inspect HTTPS pages, read encrypted content, or replace a VPN.
- Best design uses Pi-hole, encrypted upstream DNS, local caching, backups, monitoring, and a tested rollback path.
- Smart TVs, speakers, cameras, and game consoles become visible through DNS query logs.
- Allowlist narrowly, test changes, and keep router fallback ready before production use.
1. What a DNS Firewall Does
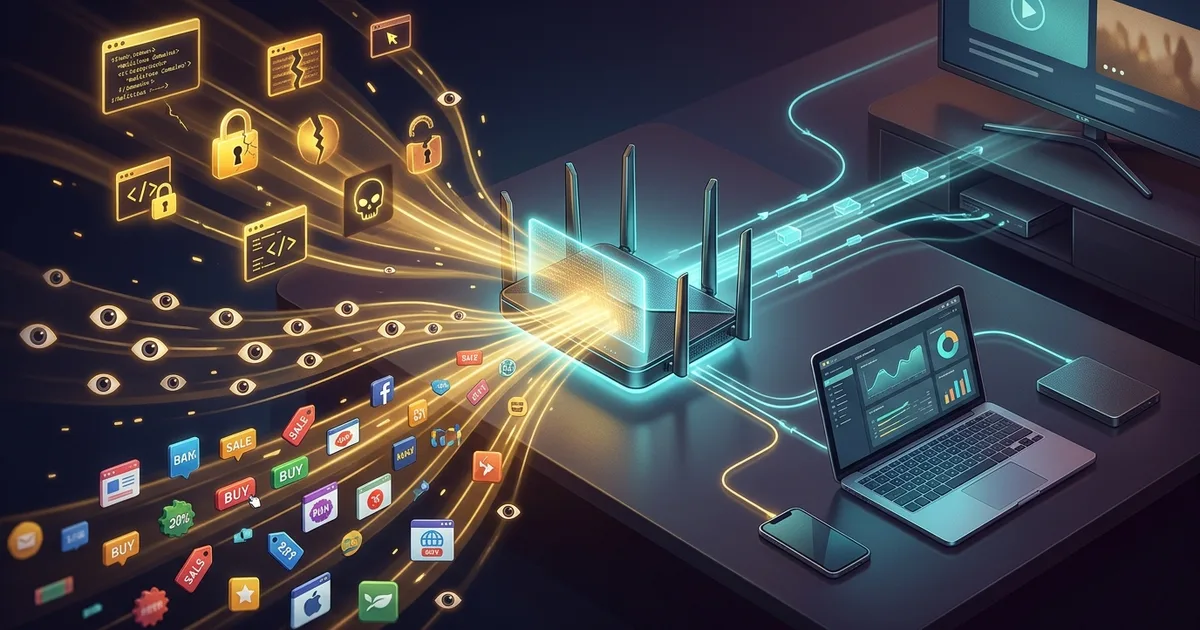
DNS translates names into IP addresses. When a device requests ads.example.com, it first asks a DNS resolver for an address. A home DNS firewall answers that request from policy.
If domain belongs to advertising, tracking, malware, or telemetry blocklist, Pi-hole returns no usable address. Browser, application, or smart device cannot connect to that domain through normal DNS resolution.
This happens before HTTP or HTTPS connection starts.
That distinction matters. DNS filtering blocks domain lookup, not every advertisement. First-party ads sharing same domain as content may load. Apps using hardcoded IP addresses may bypass DNS. Devices using DNS-over-HTTPS or DNS-over-TLS outside your network may also escape local policy.
Still, DNS filtering gives network-wide control:
- Phones receive same tracker policy.
- Smart TVs lose many analytics endpoints.
- Game consoles avoid known telemetry domains.
- IoT devices expose unexpected outbound dependencies.
- Malware domains can fail before payload retrieval.
- One policy covers devices without browser extensions.
Traditional ad blocking works inside one browser. Pi-hole works at network edge, where every DNS request passes through one decision point.
This creates an important security boundary: DNS becomes policy enforcement, not merely name lookup.
Pi-hole does not make your network anonymous. DNS queries reveal requested domains to whichever resolver receives them. Use encrypted upstream DNS to protect traffic between Pi-hole and resolver, but understand resolver operators can still see queries unless you operate recursive infrastructure yourself.
2. Architecture: Pi-hole, Recursive DNS, Encryption, Cache, and Local Names
A typical request follows this path:
- Client asks router or Pi-hole for
news.example. - Pi-hole checks local cache.
- Pi-hole checks blocklists and allowlists.
- If permitted and uncached, Pi-hole sends request to upstream resolver.
- Upstream resolver answers from its cache or performs recursion.
- Pi-hole caches response and returns address to client.
- Client opens connection to returned IP.
Pi-hole normally acts as filtering forwarder. It does not need to perform full DNS recursion. Upstream choices include:
- Public resolver using DNS-over-HTTPS or DNS-over-TLS.
- ISP resolver.
- Self-hosted recursive resolver such as Unbound.
- Managed DNS filtering service such as NextDNS.
Encrypted DNS protects resolver traffic from local network observers and some access providers. DNS-over-TLS commonly uses TCP port 853. DNS-over-HTTPS uses HTTPS, normally TCP port 443, making traffic resemble web traffic. Encryption hides query contents in transit, but it does not eliminate metadata at resolver endpoint.
A recursive resolver such as Unbound walks DNS hierarchy itself. It asks root servers, then top-level domain servers, then authoritative servers. This removes dependence on public resolver policy, but adds maintenance, cache tuning, DNSSEC validation, and troubleshooting work.
Pi-hole cache reduces repeated upstream requests. Cached positive records return quickly until TTL expires. Negative answers also cache for a period defined by authoritative DNS behavior. Cache improves resilience when upstream service has temporary trouble, but stale policy can confuse testing. Flush cache after major blocklist or DNS changes.
Local hostnames add another path. Router DHCP can assign addresses and names. Pi-hole can resolve local records such as:
nas.home.arpa       192.168.1.20
printer.home.arpa   192.168.1.30
Use home.arpa for home network names. Avoid .local when possible because multicast DNS uses it and can produce inconsistent behavior across operating systems.
Clients should receive Pi-hole address through DHCP. Router advertises Pi-hole as primary DNS. If router advertises a second public resolver, clients may choose it and bypass filtering. Configure one controlled DNS path, or enforce DNS traffic at router firewall.
Pi-hole has several decision layers:
- Exact allowlist entries.
- Exact or wildcard block rules.
- Imported blocklists.
- Local DNS records.
- Upstream forwarding.
- Cache response.
Order and configuration matter. A broad wildcard allowlist can defeat tracker protection. A broad block rule can break login, payments, streaming, or device provisioning.
Low-Level Packet, Kernel, and Protocol Behavior
DNS begins at application layer, but packet behavior determines reliability.
A client usually sends a UDP DNS query to port 53. UDP avoids connection setup and suits small request-response exchanges. Large responses, DNSSEC records, or truncated replies can trigger TCP fallback. Firewalls that permit UDP but block TCP port 53 create intermittent failures rather than clean failure.
DNS-over-TLS uses a persistent or reused TCP connection, then TLS encryption. DNS-over-HTTPS sends DNS messages inside HTTPS requests. Pi-hole receives ordinary client DNS unless clients are configured for encrypted DNS directly. Encryption between Pi-hole and upstream does not encrypt client-to-Pi-hole traffic on local network.
The Linux kernel tracks sockets through conntrack. NAT routers maintain state for DNS flows. If Pi-hole runs inside Docker, published ports, bridge networking, and host firewall rules affect packet delivery. A container listening on 127.0.0.1 cannot serve other LAN hosts. A service bound to all interfaces can expose DNS beyond home network if firewall rules fail.
DNS uses TTL values to control cache lifetime. Short TTL increases upstream activity and policy freshness. Long TTL reduces requests and improves resilience but delays record changes. Pi-hole cannot override every client-side cache. Browsers, operating systems, and applications maintain their own DNS caches.
IPv6 creates another path. A router can advertise IPv6 DNS through Router Advertisements even when DHCPv4 points to Pi-hole. Configure IPv6 DNS deliberately or clients may bypass filter over IPv6.
Trade-offs are clear:
- More blocklists increase coverage but also false positives.
- Encrypted upstream improves privacy from local observers but creates resolver trust.
- Recursive DNS reduces public-resolver dependence but increases operations.
- Local DNS control improves visibility but creates single-service failure risk.
- Router enforcement improves policy compliance but can break captive portals and troubleshooting.
3. Benchmark: Hosts File, Browser Extension, Pi-hole, and NextDNS
| Method | Coverage | Latency behavior | Maintenance | Main limit |
|---|---|---|---|---|
| Hosts file | One device; all applications using system resolver | Local lookup; large files can add lookup cost | Manual or script-based | Poor central control |
| Browser extension | One browser and profile | Usually low; page inspection adds work | Extension and filter updates | Misses apps and IoT |
| Pi-hole | Whole LAN using configured DNS | Local cache often reduces repeated lookup delay | Blocklists, backups, updates | Bypass and false positives |
| NextDNS | Devices configured through service or profile | Depends on network and resolver path | Managed blocklists and logs | Account, policy, and provider dependency |
Hosts files map names locally. They cannot easily express modern policy, inspect query behavior centrally, or protect devices without local file access.
Browser extensions can remove page elements, cosmetic content, and scripts after page load. They offer stronger browser-level control than DNS for same-domain advertising. They do not protect smart TVs, mobile applications, or game consoles.
Pi-hole provides ownership and LAN-wide visibility. It needs a stable host, updates, backups, and careful policy management.
NextDNS shifts infrastructure work to managed service. It offers encrypted DNS, profiles, analytics, and roaming device policies. It reduces home-server failure risk but transfers trust and availability dependence to provider.
Do not compare only lookup speed. Measure policy coverage, failure recovery, device support, encrypted transport, bypass resistance, and operational effort. A fast resolver that breaks banking authentication has poor practical performance.
4. Production Setup
Choose hardware that stays online: small Linux host, existing server, virtual machine, or container host. A Raspberry Pi-class device usually handles home DNS easily. CPU demand remains low; one CPU core is enough for ordinary household traffic, while storage reliability and network availability matter more.
Keep Pi-hole on wired Ethernet when possible. Wi-Fi sleep, roaming, and access-point failure can turn DNS into a household outage.
ASCII Network Diagram
                    encrypted DNS
                       TCP 853
                         |
                         v
[Phone]       [Pi-hole] ---> [Upstream Resolver]
[TV] ---------   |                 |
[Console] ----   |                 +--> public recursive service
[IoT] ---------- |                 or self-hosted Unbound
                 |
             local DNS
                 |
        [Router DHCP / Firewall]
                 |
              Internet
Install native service for fewer moving parts. Use Docker when existing operations already manage Compose, volumes, updates, and host firewall rules.
Minimal Compose example:
services:
  pihole:
    image: pihole/pihole:latest
    container_name: pihole
    environment:
      TZ: UTC
      FTLCONF_webserver_api_password: change-this
      FTLCONF_dns_upstreams: 1.1.1.1;1.0.0.1
    volumes:
      - ./etc-pihole:/etc/pihole
      - ./etc-dnsmasq.d:/etc/dnsmasq.d
    ports:
      - "53:53/tcp"
      - "53:53/udp"
      - "80:80/tcp"
    restart: unless-stopped
Replace password and upstream choices before deployment. Do not expose DNS or admin interface to public Internet. Restrict management interface to LAN or trusted administration network.
Encrypted upstream configuration varies by deployment. Pi-hole can forward to a local DNS-over-HTTPS or DNS-over-TLS proxy. Unbound can provide recursive DNS locally. The design goal: clients speak DNS to Pi-hole; Pi-hole sends protected or independently recursive queries upstream.
Back up configuration, not merely container image. Preserve Pi-hole settings, custom DNS records, allowlists, blocklists, DHCP state, and Compose files. Test restore on another host. A backup never tested is a hope file.
Useful checks:
dig @192.168.1.10 example.com
dig @192.168.1.10 doubleclick.net
docker compose logs --tail=100 pihole
Expected result: normal domain resolves; blocked domain returns 0.0.0.0, ::, or no usable answer according to configuration. Logs show received queries and selected action.
Change router DHCP DNS to Pi-hole address. Renew leases on clients. Test wired, wireless, IPv4, and IPv6 clients separately.
5. Failure Modes and SRE Trade-Offs
False positives
Blocklists can classify required domains as advertising or telemetry. Symptoms include broken login, blank application pages, failed payments, missing thumbnails, or IoT onboarding failure.
Use query logs to identify exact failed domain. Allowlist one narrow domain, then retest. Avoid allowing parent domains when one hostname fixes issue.
DNS outage
If Pi-hole host fails, clients lose name resolution. Keep a documented rollback:
- Change router DHCP DNS to trusted resolver.
- Renew client leases or reconnect devices.
- Confirm normal resolution.
- Repair Pi-hole.
- Restore Pi-hole advertisement only after tests pass.
Do not configure public DNS as silent secondary unless accepting bypass. Secondary DNS improves availability but weakens enforcement because clients may choose either server.
Captive portals
Hotels, guest networks, and some public Wi-Fi systems redirect DNS or HTTP to login pages. Strict local DNS can interfere with detection. Disable custom DNS temporarily or use network-provided DNS until authentication completes.
Bypass
Clients may use hardcoded DNS, DNS-over-HTTPS, DNS-over-TLS, VPN tunnels, or direct IP addresses. Router firewall can redirect outbound port 53 to Pi-hole, block external port 53, and restrict port 853. Blocking HTTPS-based DNS is harder because it shares port 443.
VPN policy needs explicit design. Force DNS through VPN provider, route Pi-hole through tunnel, or accept that VPN endpoint controls DNS. Avoid assuming local filtering survives every tunnel.
Observability
Track:
- Pi-hole process health.
- DNS query success rate.
- Upstream response time.
- Block percentage.
- Cache hit ratio.
- Disk use.
- CPU and memory.
- IPv4 and IPv6 behavior.
- Top clients and blocked domains.
Export logs carefully. DNS logs can reveal household behavior. Set retention limits, restrict dashboard access, and encrypt backups.
6. Smart Home Case: Exposing Hidden DNS Traffic
A smart TV may contact analytics, advertising, update, crash-reporting, and content-delivery domains every few minutes. Without central DNS logs, these requests remain invisible.
Install Pi-hole, assign it through DHCP, then identify the TV by client IP or DHCP hostname. Let device operate normally for one day. Filter query logs by client. Group domains by function:
- Firmware and update services.
- Authentication and account services.
- Content delivery.
- Advertising.
- Analytics and telemetry.
- Time synchronization.
- Certificate or provisioning services.
Block obvious advertising and tracking domains first. Observe failures. If streaming breaks, inspect the last blocked query before failure. Allowlist exact required hostname, not entire provider domain.
Example reasoning:
metrics.vendor.example       likely telemetry
ads.vendor.example           advertising
login.vendor.example         authentication
cdn.vendor.example           content delivery
update.vendor.example        firmware
Names alone do not prove function. Check timing, device documentation, and repeated behavior. A domain called metrics may support device health. A domain called cdn may deliver both content and advertising.
Create a device-specific policy when supported. Smart TV needs different rules from work laptop. Never use one permissive global allowlist to fix one broken device.
After allowlisting, repeat test:
- Cold boot.
- Account login.
- Streaming playback.
- Firmware check.
- Sleep and wake.
- Factory reset or onboarding if relevant.
Record each rule with reason and date. Remove rules after vendor behavior changes.
7. Security Boundaries
DNS filtering reduces exposure but does not replace endpoint security, patching, browser protection, or firewall policy.
HTTPS prevents Pi-hole from reading page contents, passwords, cookies, and request bodies. Pi-hole sees domain queries such as api.example.com, not encrypted URL paths or response content. Domain names still reveal meaningful metadata.
DNSSEC validates authenticity of DNS data when enabled and supported. It does not hide queries. Encryption hides transport content from intermediaries but does not prove endpoint trust.
Pi-hole itself becomes infrastructure. Protect admin credentials, update software, limit dashboard access, monitor disk space, and avoid public exposure. Never run open recursive DNS resolver on Internet-facing interface.
Frequently Asked Questions (FAQ)
Does DNS blocking stop a VPN?
No. VPN software usually captures device traffic and sends it through an encrypted tunnel. DNS may travel inside that tunnel to VPN provider resolver, bypassing Pi-hole. Some VPN clients allow custom DNS or split tunneling, while others force their own resolver. Enforce local DNS only for traffic that remains on your LAN. For stronger control, choose VPN software with explicit DNS policy and firewall kill-switch behavior.
Can Pi-hole read HTTPS traffic?
No. Pi-hole reads DNS queries and responses, not encrypted HTTPS content. It can see requested domain names because clients resolve domains before connecting, but it cannot read URL paths, page content, passwords, cookies, or message bodies. HTTPS inspection requires endpoint certificates and proxy deployment, which creates major security, privacy, and compatibility costs. DNS filtering remains a narrower, safer control.
Will Pi-hole increase gaming ping?
Usually, no. DNS lookup happens before connection establishment, and Pi-hole cache can make repeated lookups fast. Pi-hole does not sit inside game packet paths after address resolution. Ping can increase if DNS is slow during server discovery or if filtering blocks matchmaking services. Test with and without Pi-hole using the same game server. Do not measure DNS lookup time as gameplay latency.
How does Pi-hole protect mobile devices?
Mobile devices use Pi-hole when connected to networks that advertise Pi-hole through DHCP or router configuration. Cellular traffic does not pass through home DNS unless device VPN or mobile profile routes it there. Private DNS, DNS-over-HTTPS, VPN applications, and hardcoded resolvers can bypass local filtering. Use managed device profiles, VPN-based filtering, or NextDNS roaming policies for protection away from home.
How do I recover if DNS filtering breaks my network?
Use router administration to replace Pi-hole DNS with trusted resolver addresses, then renew client leases or reconnect devices. Keep router access credentials and rollback steps offline. If router control is unavailable, temporarily set DNS on one test device to verify recovery. Repair Pi-hole, inspect logs, and restore only after normal resolution works. Never delete configuration before exporting settings and custom local records.
Conclusion
Home DNS filtering moves ad and tracker control from individual browsers to network edge. Pi-hole combines policy, caching, local names, and visibility in one small service. Encrypted upstream DNS protects resolver traffic; recursive DNS reduces public-provider dependence; logs reveal hidden smart-home behavior.
Good deployment depends less on aggressive blocklists than on disciplined operations: narrow allowlists, backups, IPv6 awareness, monitoring, and tested rollback. Treat DNS as production infrastructure. One failed resolver can make every connected device appear offline.
Explore network behavior through AI Playground and project simulations.