 Atlas Network Engineer • • 1,278 words • 7 min read
OpenRoaming Explained: The End of Wi-Fi Login Pages Is Here
OpenRoaming and Passpoint let your phone join airport and café Wi-Fi automatically and securely. Learn how it works and why captive portals are vanishing.
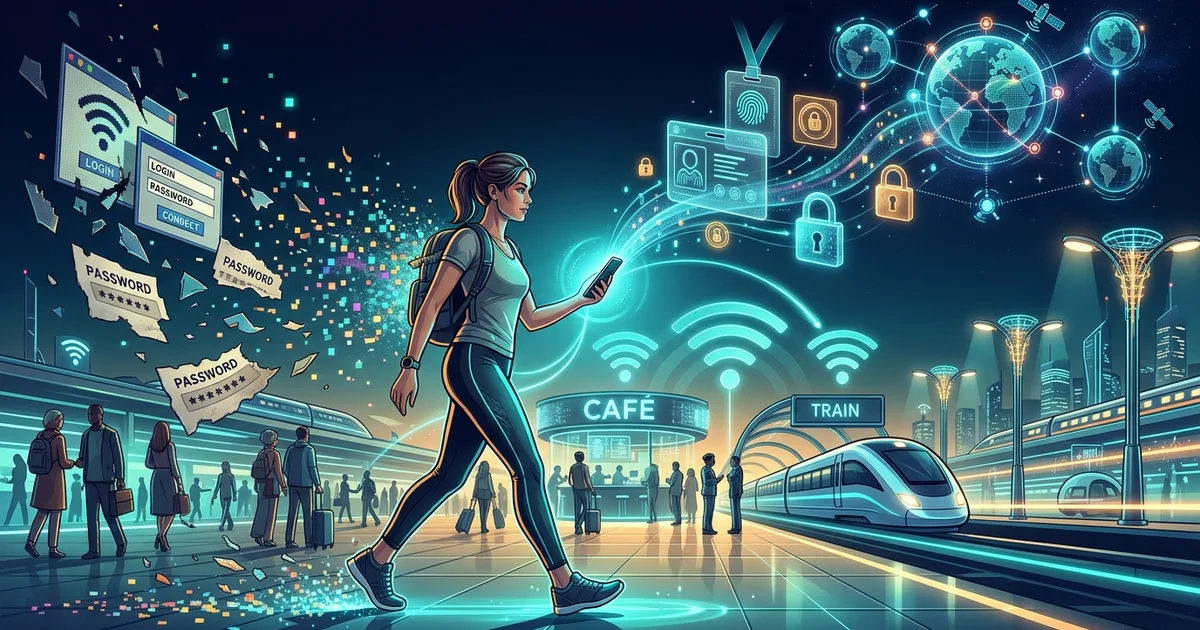
TL;DR (Direct Answer): OpenRoaming and Passpoint (also called Hotspot 2.0) let your phone join public Wi-Fi automatically and securely, with no login page or password. Your device proves who it is with a trusted digital identity, much like a SIM card does on mobile networks. Each user gets private encryption, so fake hotspots and phishing login pages stop working. Airports, cafés, hotels and cities are already rolling it out worldwide.
Why Public Wi-Fi Feels Like a Hotel With a Form at Every Door
Imagine a hotel that makes you fill out a form at every door: the lobby, the elevator, your room. That is public Wi-Fi today. You find the network, open a login page, accept terms you never read, and type your email. Then you walk to the next gate and do it all again.
Mobile carriers solved this decades ago with roaming, where your SIM card acts as a passport. You land in a new country and your phone just works. Passpoint is a Wi-Fi standard that brings this passport logic to hotspots. OpenRoaming is a global network of providers built on top of it.
This is about safety, not just convenience. A fake network called "Free_Airport_WiFi" is easy to create. When your phone stops trusting network names and starts checking real identities, those traps lose their power.
How OpenRoaming Works, Step by Step
Reading the sticker on the door
Before connecting, your phone quietly asks nearby access points, "Which identity providers do you accept?" This uses ANQP (Access Network Query Protocol), a pre-connection question. It is like reading a shop's "we accept Visa" sticker before walking in.
Showing your passport
Your phone checks whether it holds a matching profile from a carrier, Google, Samsung, Cisco, or a university's eduroam account. It then proves its identity cryptographically through WPA3/WPA2-Enterprise and 802.1X/EAP, the same login system corporate offices use. No typing, just certificates or SIM credentials.
The trust club
The Wireless Broadband Alliance (WBA), an industry group, runs the OpenRoaming federation. Its certificates confirm that both the café network and your identity provider are genuine members.
Your own private lock
Every user gets a unique encryption key. The person at the next table cannot snoop on your traffic. Walk into any member location worldwide, and you reconnect silently.
Comparing Your Public Wi-Fi Options
| Option | Encrypted over the air? | Fake hotspot risk | Effort for you | Main catch |
|---|---|---|---|---|
| Open network + login page | No | High | Log in everywhere | Pages break on phones |
| Shared password on a chalkboard | Yes, but shared | Medium | Type once per venue | Everyone shares one trust zone |
| Eduroam | Yes, per user | Low | Set up once | Universities only |
| Passpoint (carrier profile) | Yes, per user | Low | None | Tied to carrier partners |
| OpenRoaming | Yes, per user | Low | Set up once | Uneven device and venue support |
What does this mean for you? Login pages are easy for venues and great for marketing data, but weakest for you. OpenRoaming is global and identity-based. It even offers privacy levels, including anonymous access. The trade-off: many venues haven't upgraded their hardware yet, and you must trust the provider you choose.
A Traveler Lands in Istanbul
Here is what happens in the two seconds after your plane lands:
Phone ──(ANQP: "Do you accept OpenRoaming?")──► Airport Access Point
      ◄──("Yes" – RCOI match)──────────────────┘
Phone ══ Encrypted EAP tunnel ══► Airport RADIUS server
                                       │
                         OpenRoaming certificate check
                                       │
                         Your identity provider (Google / carrier)
                                       │
                                  "Approved"
                                       │
               Unique encryption key ──► Online, zero taps
This diagram shows your phone confirming the network is real before sending any personal data. RCOI is simply the ID tag for a roaming group. RADIUS is the server that checks your credentials. If you enjoy seeing invisible systems like this in motion, explore our Interactive Engineering Simulations.
Your quick checklist
- Android: Look in Wi-Fi settings for "Passpoint" or "Hotspot 2.0" (often under Advanced or Saved networks).
- iPhone: Carrier profiles install automatically. Check Wi-Fi network details and Settings > General > VPN & Device Management.
- Install OpenRoaming profiles only from trusted providers, such as your phone maker or carrier.
- Remove unwanted profiles from the same menus.
Myths, Mistakes, and a Three-City Trip
"Automatic means insecure." The opposite is true. Enterprise-grade authentication and per-user encryption beat a café login page.
"HTTPS makes this pointless." HTTPS protects page contents. Network encryption also hides DNS lookups (your device's website "phone book" requests), background chatter and metadata.
"The venue sees my identity." At higher privacy levels, it sees only an anonymous token.
Common mistakes include installing random profiles from unknown sites, which is like handing someone a master key. Also don't assume every big-venue "free Wi-Fi" is OpenRoaming; check the lock icon. Keep your VPN if you need one, since OpenRoaming protects only the local hop.
Picture a consultant flying from Heathrow, then by train, then to a Tokyo hotel. Before, she typed her email into five portals and fell for a lookalike hotspot. Now, her device hops between airport, rail and hotel networks, verifying each certificate first. Connectivity becomes a utility, like electricity. Explore more ideas in our AI Playground.
Frequently Asked Questions (FAQ)
Does my phone support OpenRoaming or Passpoint, and how can I check?
Most Android phones from roughly the last several years and iPhones running modern iOS support Passpoint. On Android, look for "Passpoint" or "Hotspot 2.0" in Wi-Fi settings. On iPhone, carrier profiles install quietly in the background. OpenRoaming specifically requires a profile from a participating provider, such as a phone maker, carrier or app. Without one, your phone supports the technology but won't automatically join OpenRoaming networks.
Is OpenRoaming free, and who pays for the connection?
OpenRoaming supports both free "settlement-free" access and paid models. Venues like airports, malls and cafés often offer it free because good Wi-Fi attracts visitors and keeps them longer. Mobile carriers also pay or partner to shift your data from crowded cell towers onto Wi-Fi, saving their network capacity. For most travelers, it costs nothing extra beyond the identity profile they already have.
Can the café or airport see which websites I visit?
They see less than on open Wi-Fi. Per-user encryption stops nearby people from eavesdropping on the air between your phone and the access point. However, the venue's network still carries your traffic onward to the internet. HTTPS hides page contents, and encrypted DNS hides which sites you look up. Together, those layers keep your browsing far more private than a traditional login-page hotspot.
Do I still need a VPN on OpenRoaming networks?
Not for protection against local, over-the-air snooping, because OpenRoaming already encrypts that hop with a unique key. A VPN can still be useful, though. It hides your traffic from the venue's network operator and your internet provider. It also helps when you need a different virtual location for streaming or work systems. Think of OpenRoaming as locking your front door, and a VPN as an armored car.
Will login pages and Wi-Fi passwords disappear completely?
Not overnight. Many venues still run older access points that can't support Passpoint. Some businesses rely on login pages to collect marketing emails, and some countries require user logging that portals handle easily. Those factors will keep captive portals around for years. Still, the direction is clear: major airports, hotel chains, carriers and cities are moving toward identity-based Wi-Fi that works invisibly, just like cellular roaming.